ProductIn development
Codeward
Cyber Resilience Act workspace for small software and device makers. Checks SBOMs, finds components with exploited vulnerabilities and tracks every Article 14 reporting deadline.
Highlights
- 25 SBOM checks across CRA, CISA and BSI
- Exploited vulnerability matching with OSV and CISA KEV
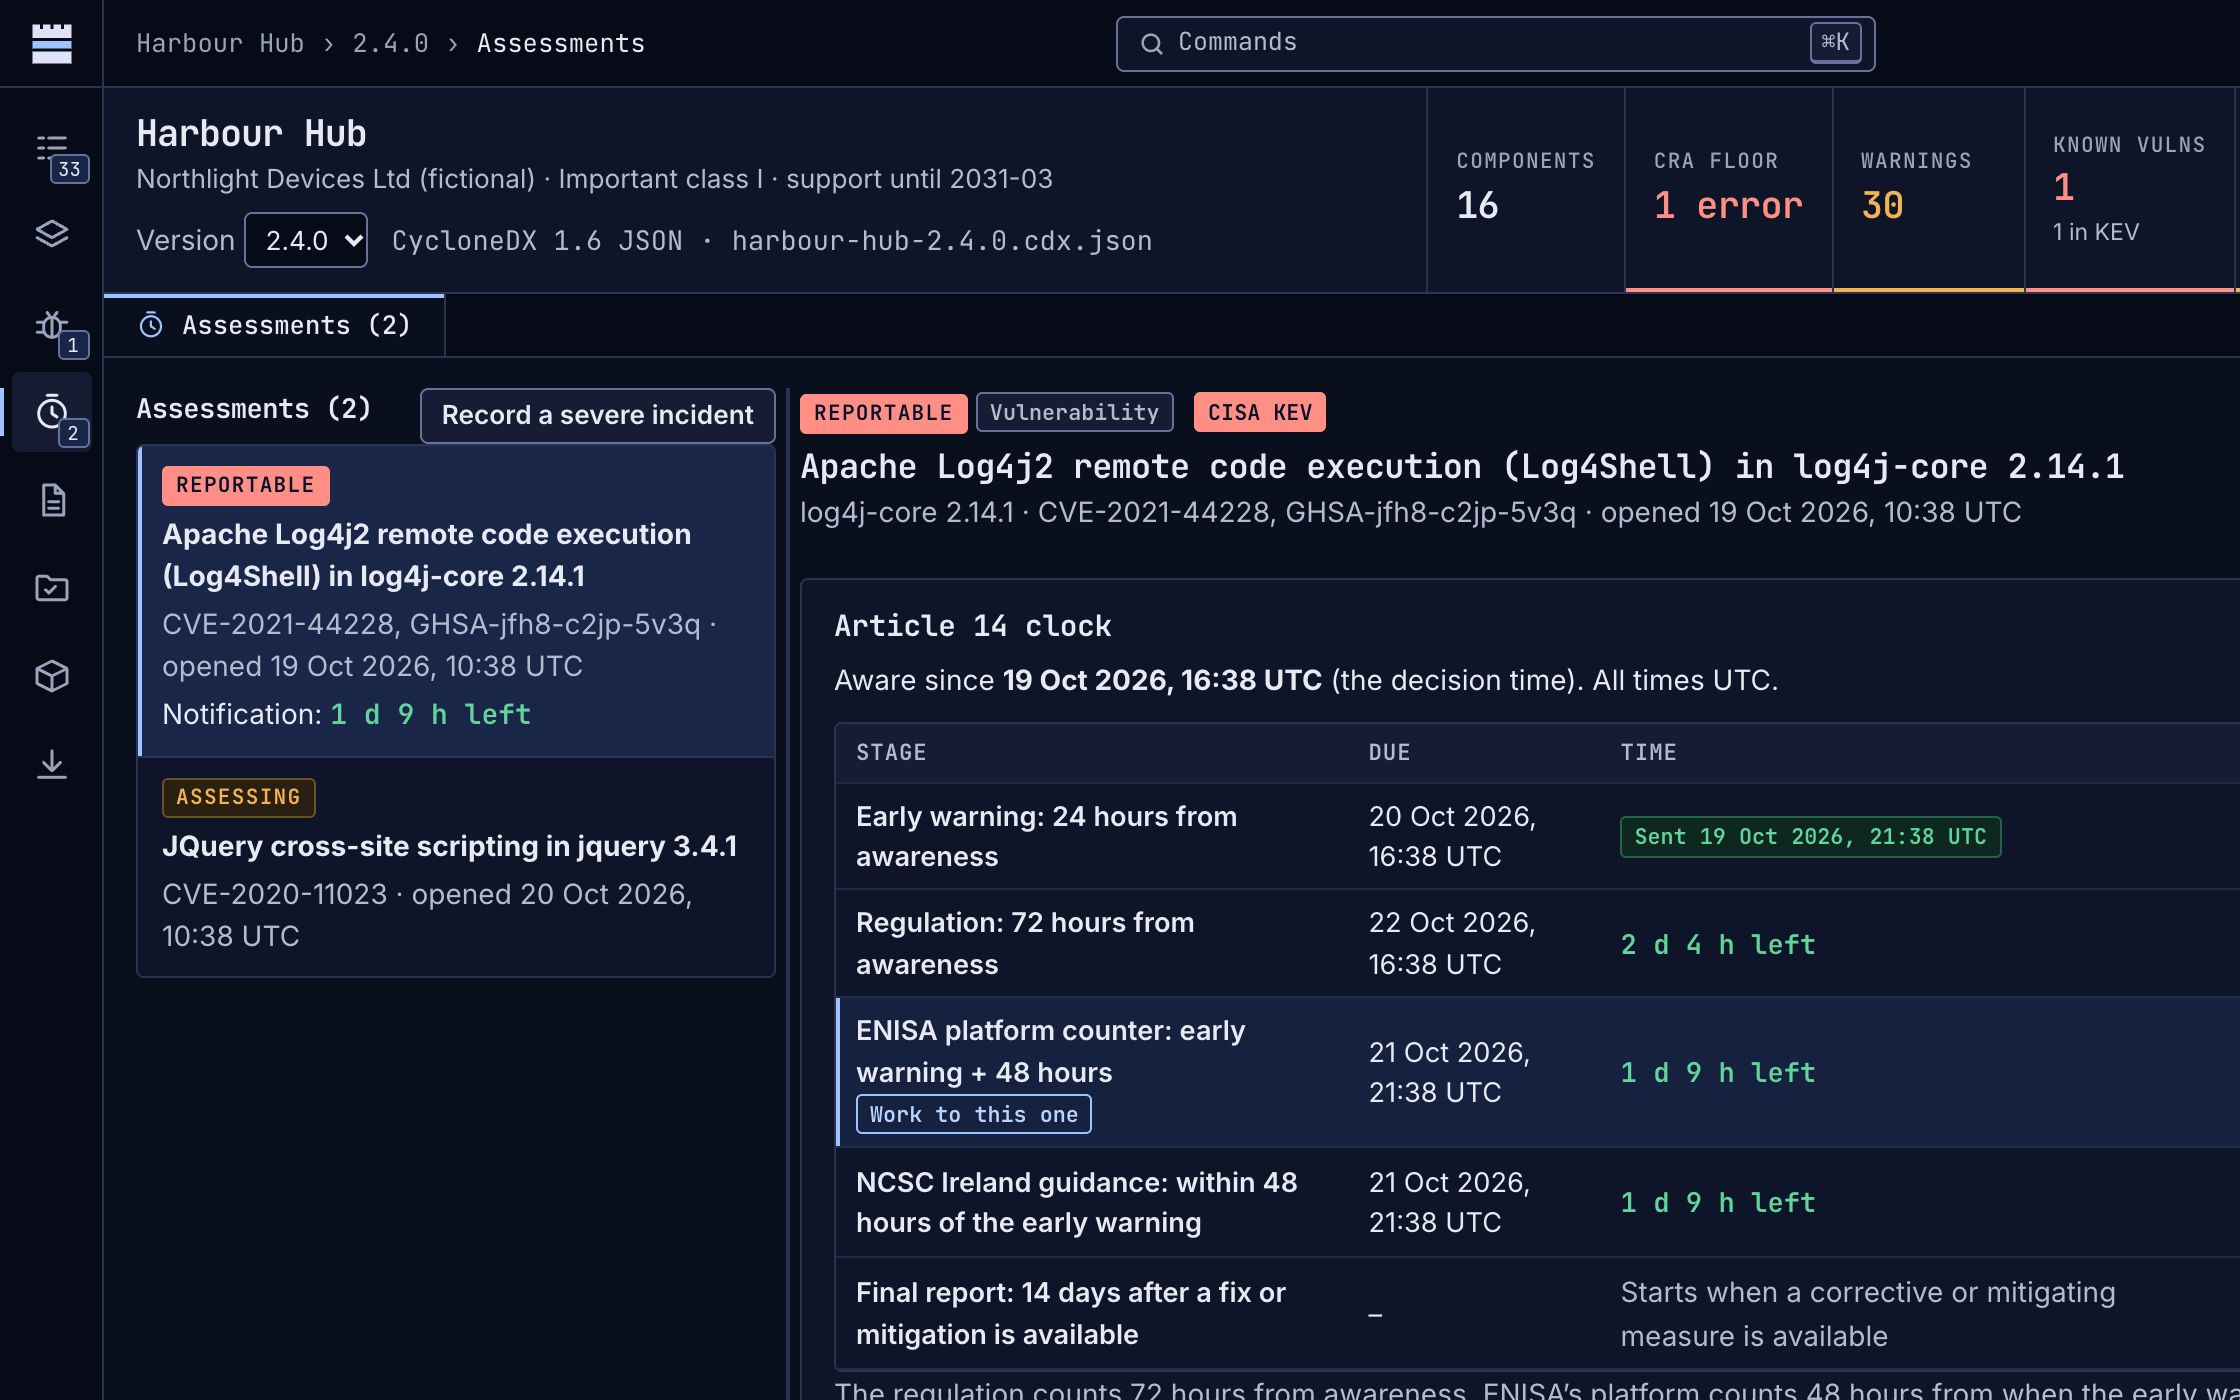
- Article 14 clocks and ENISA report drafts
- Annex VII and Annex I checklists
Codeward reads CycloneDX and SPDX SBOMs and checks them against the CRA, the 2026 CISA minimum elements and the BSI guideline. It matches components against OSV.dev and the CISA Known Exploited Vulnerabilities catalogue.
When a vulnerability is reportable it starts the 24 hour and 72 hour clocks and drafts ENISA reports that fit the platform's field limits. SBOMs stay in the browser; only package identifiers are sent for matching.
Pre-launch: register interest on the site.
Keep exploring
Related solutions.
ProductIn development
Embertally
EU and UK CBAM cost and supplier data. Checks the templates suppliers send, costs every customs line on default values and on verified data, and shows which suppliers to chase first.
